Category

Tech

Category

Two companies can send identical emails on the same day, and only one of them reaches the inbox. The difference usually has nothing to do with the message itself. The real answer often traces back to a handful of DNS records that most people never look at. For anyone running professional email services, these records determine whether a message reaches its destination or disappears before a reader ever sees it.

DNS configuration is often overlooked as a minor technical detail located inside a control panel, but it plays a direct role in whether a domain builds trust with mail servers across the internet. Business email service providers rely on these same records to authenticate outgoing messages and confirm a sender is legitimate. Without them, even a well-written email risks never being read.

How does DNS work for email?

Every email carries more information than the subject line and body suggest. Behind that message travels a set of DNS records that tell the receiving servers who sent it, whether it was tampered with in transit, and whether the sending domain has a history worth trusting. Mail servers check these records within milliseconds, deciding a message’s destination before a human ever opens their inbox. A domain with clean, complete records earns a smoother path into the inbox, while one with gaps starts every send at a disadvantage.

SPF Records and Sender Verification

An SPF record lists every server permitted to send mail on behalf of a domain. If a receiving server sees an email coming from an address that isn’t listed, it treats the message as suspicious and often sends it straight to spam. SPF only works when every legitimate sending source is listed correctly, marketing platforms and CRM tools included, not just the primary mail server.

DKIM and Message Integrity

DKIM adds a unique digital signature to every outgoing email, allowing the recipient’s mail server to verify that the message has not been altered during transit. Destination servers match this signature against a public key published in DNS. A mismatch signals tampering, and the message loses credibility instantly. Domains without DKIM configured send messages that appear unverified by comparison, even when nothing is actually wrong with them.

DMARC and Inbox Trust

DMARC ties SPF and DKIM together and tells receiving servers what to do when a message fails: either check it, reject it, quarantine it, or deliver it anyway. Domains without a DMARC policy leave that decision to the receiving server’s judgment, which varies significantly between providers. A properly configured DMARC record removes that guesswork and gives senders real influence over delivery outcomes, instead of leaving the success of every campaign up to individual mail providers.

Reverse DNS and IP Reputation

Reverse DNS maps an outbound IP address to a specific domain name, and the absence of this record prompts strict validation filtering by recipient mail servers. Industry data suggests a meaningful share of authentication failures trace directly back to missing or mismatched reverse DNS records. It is a smaller detail compared with SPF or DKIM, yet it still shapes reputation over time, especially for domains sending high volumes of mail daily.

Common Misconfigurations that Hurt Deliverability

Duplicate SPF records, expired DKIM keys, and DMARC policies left in monitoring mode indefinitely are among the most frequent issues found during domain audits. Each one appears harmless individually, yet together they quietly damage a domain’s sending reputation. Reviewing DNS records every few months catches these problems long before they start affecting actual delivery rates and inbox placement. Small businesses without a dedicated IT team regularly encounter domain misconfigurations because administrative staff rarely modify the records after initial deployment.

Why consistent monitoring matters?

DNS records are not a configure-once routine. Mail providers regularly update their authentication requirements, and a policy that worked well two years ago may now fall short of current standards. Google’s bulk sender guidelines require domains exceeding five thousand messages a day to have SPF, DKIM, and DMARC properly configured for reliable inbox placement.

What Poor DNS Configuration Costs a Business?

A missing or outdated DNS record rarely shows up as an obvious error. Instead, open rates quietly decline, sales outreach goes unanswered, and support tickets escalate without explanation, while the actual cause remains unnoticed in a domain’s DNS settings. Marketing teams often spend weeks testing subject lines and send times before anyone checks whether the underlying authentication records are even correct.

How to Review and Correct DNS Records?

Checking DNS health does not require advanced tools. Most domain registrars and hosting dashboards display SPF, DKIM, and DMARC records directly, and free online checkers confirm whether each one is valid. MilesWeb provides free professional email accounts along with daily backups, giving businesses a foundation where authentication and message security are handled correctly from the start.

Concluding Insights

DNS may operate quietly in the background, but it decides whether a message reaches an inbox or disappears without a trace. Businesses that review SPF, DKIM, and DMARC on a regular basis protect years of sender reputation with very little ongoing effort. MilesWeb pairs this reliability with free professional email accounts and daily backups, making dependable delivery a built-in part of the service rather than an afterthought.

Handling these small technical details early builds a communication channel worth trusting for years ahead, one message at a time. A well-configured domain does not need constant attention once it is set up correctly, only a periodic check to confirm nothing has quietly drifted out of place.
Article image

Two companies can send identical emails on the same day, and only one of them reaches the inbox. The difference usually has nothing to do with the message itself. The real answer often traces back to a handful of DNS records that most people never look at. For anyone running professional email services, these records determine whether a message reaches its destination or disappears before a reader ever sees it.

DNS configuration is often overlooked as a minor technical detail located inside a control panel, but it plays a direct role in whether a domain builds trust with mail servers across the internet. Business email service providers rely on these same records to authenticate outgoing messages and confirm a sender is legitimate. Without them, even a well-written email risks never being read.

How does DNS work for email?

Every email carries more information than the subject line and body suggest. Behind that message travels a set of DNS records that tell the receiving servers who sent it, whether it was tampered with in transit, and whether the sending domain has a history worth trusting. Mail servers check these records within milliseconds, deciding a message’s destination before a human ever opens their inbox. A domain with clean, complete records earns a smoother path into the inbox, while one with gaps starts every send at a disadvantage.

SPF Records and Sender Verification

An SPF record lists every server permitted to send mail on behalf of a domain. If a receiving server sees an email coming from an address that isn’t listed, it treats the message as suspicious and often sends it straight to spam. SPF only works when every legitimate sending source is listed correctly, marketing platforms and CRM tools included, not just the primary mail server.

DKIM and Message Integrity

DKIM adds a unique digital signature to every outgoing email, allowing the recipient’s mail server to verify that the message has not been altered during transit. Destination servers match this signature against a public key published in DNS. A mismatch signals tampering, and the message loses credibility instantly. Domains without DKIM configured send messages that appear unverified by comparison, even when nothing is actually wrong with them.

DMARC and Inbox Trust

DMARC ties SPF and DKIM together and tells receiving servers what to do when a message fails: either check it, reject it, quarantine it, or deliver it anyway. Domains without a DMARC policy leave that decision to the receiving server’s judgment, which varies significantly between providers. A properly configured DMARC record removes that guesswork and gives senders real influence over delivery outcomes, instead of leaving the success of every campaign up to individual mail providers.

Reverse DNS and IP Reputation

Reverse DNS maps an outbound IP address to a specific domain name, and the absence of this record prompts strict validation filtering by recipient mail servers. Industry data suggests a meaningful share of authentication failures trace directly back to missing or mismatched reverse DNS records. It is a smaller detail compared with SPF or DKIM, yet it still shapes reputation over time, especially for domains sending high volumes of mail daily.

Common Misconfigurations that Hurt Deliverability

Duplicate SPF records, expired DKIM keys, and DMARC policies left in monitoring mode indefinitely are among the most frequent issues found during domain audits. Each one appears harmless individually, yet together they quietly damage a domain’s sending reputation. Reviewing DNS records every few months catches these problems long before they start affecting actual delivery rates and inbox placement. Small businesses without a dedicated IT team regularly encounter domain misconfigurations because administrative staff rarely modify the records after initial deployment.

Why consistent monitoring matters?

DNS records are not a configure-once routine. Mail providers regularly update their authentication requirements, and a policy that worked well two years ago may now fall short of current standards. Google’s bulk sender guidelines require domains exceeding five thousand messages a day to have SPF, DKIM, and DMARC properly configured for reliable inbox placement.

What Poor DNS Configuration Costs a Business?

A missing or outdated DNS record rarely shows up as an obvious error. Instead, open rates quietly decline, sales outreach goes unanswered, and support tickets escalate without explanation, while the actual cause remains unnoticed in a domain’s DNS settings. Marketing teams often spend weeks testing subject lines and send times before anyone checks whether the underlying authentication records are even correct.

How to Review and Correct DNS Records?

Checking DNS health does not require advanced tools. Most domain registrars and hosting dashboards display SPF, DKIM, and DMARC records directly, and free online checkers confirm whether each one is valid. MilesWeb provides free professional email accounts along with daily backups, giving businesses a foundation where authentication and message security are handled correctly from the start.

Concluding Insights

DNS may operate quietly in the background, but it decides whether a message reaches an inbox or disappears without a trace. Businesses that review SPF, DKIM, and DMARC on a regular basis protect years of sender reputation with very little ongoing effort. MilesWeb pairs this reliability with free professional email accounts and daily backups, making dependable delivery a built-in part of the service rather than an afterthought.

Handling these small technical details early builds a communication channel worth trusting for years ahead, one message at a time. A well-configured domain does not need constant attention once it is set up correctly, only a periodic check to confirm nothing has quietly drifted out of place.
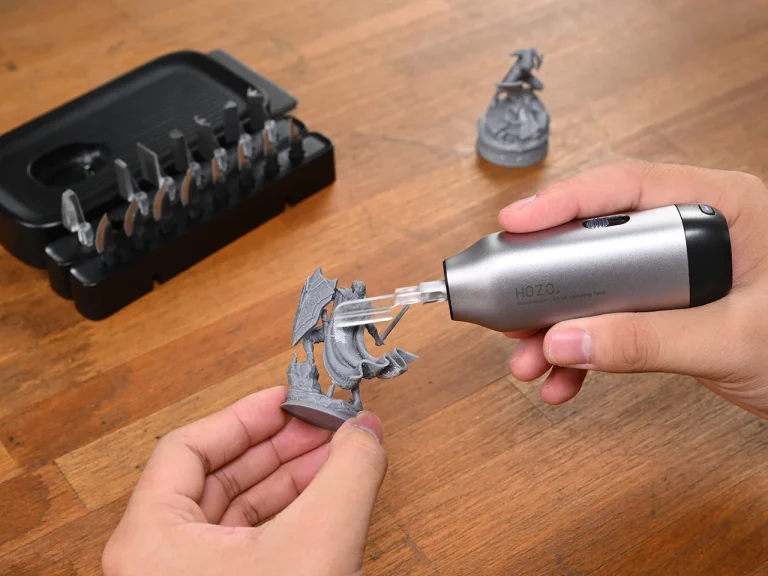
The detail sander market is crowded with options that look capable on a product page but disappoint in actual use. Insufficient motor power, vibration that causes hand fatigue within minutes, poor dust extraction that fills the workshop in seconds, and pad attachment systems that feel fragile under repeated abrasive changes — these are the frustrations that drive experienced woodworkers and DIYers to approach detail sander purchases with significant scepticism.

The HOZO NeoSander enters this category with a design that addresses the specific complaints most commonly raised about detail sanding tools. Understanding what sets it apart from the alternatives starts with understanding what actually matters in this tool category.

Motor Performance: The Foundation of Everything

A detail sander motor has to work harder per unit of pad surface than a large orbital sander, because the smaller pad concentrates the sanding action in a much smaller area. An underpowered motor bogs down under any meaningful sanding pressure, producing inconsistent results and extending the time needed to complete even straightforward tasks.

The NeoSander delivers consistent orbital action at a rate that handles both fine finishing work and the more demanding removal passes that prepare surfaces before final smoothing. The motor maintains its speed under load rather than slowing when the tool meets resistance — a distinction that becomes very apparent when working with denser hardwoods or through old finish layers.

Ergonomics and Extended Use Comfort

Detail sanding projects rarely involve a single quick pass. Restoring a set of chairs, finishing a cabinet with multiple moulded profiles, or working through the detailed joinery on a staircase installation can mean continuous detail sanding over extended sessions. A tool that causes hand fatigue within twenty minutes is not suitable for this work, regardless of its performance on shorter tasks.

The HOZO HoZo detail sander is balanced and sized for comfortable extended use. The grip positions naturally for both the overhand hold used for flat surface work and the side grip that works better when getting into tight corner sections. The vibration level is managed effectively — the tool produces the tactile feedback needed to understand what the abrasive is doing without the numbing vibration that characterises less well-engineered alternatives.

The Premium Combo System

The premium combo designation reflects the accessory set that accompanies the tool. Different sanding profiles — the standard triangle, narrower pointed profiles for getting into tighter sections, and finger-style extensions for the narrowest reaches — expand the tool’s effective range beyond what a standard single-pad tool can address.

This versatility is particularly valuable for complex restoration projects where a single workpiece might involve both broad flat sections that benefit from the standard triangular pad and deeply recessed carved or moulded areas that require a more aggressive profile to reach effectively.

Dust Extraction Performance

The dust extraction system on a detail sander matters more than on larger tools because the tight spaces where detail work happens tend to accumulate dust quickly, obscuring the surface and affecting visibility of the work progress. The NeoSander’s extraction ports are positioned to draw dust effectively during normal working operation, keeping the surface cleaner between passes and reducing the overall airborne dust in the work area.

For use in enclosed spaces or on materials where dust is a health concern, connection to an external dust extractor is straightforward. The extraction port accepts standard hose fittings, making integration with workshop dust collection systems simple to achieve.

Who This Tool Is For

The NeoSander Premium Combo suits woodworkers who do meaningful detail work regularly — furniture makers, restoration specialists, cabinetmakers, and serious DIYers who understand that the quality of the detail sanding is what ultimately determines whether a finishing project looks genuinely professional or merely acceptable. For occasional light use, a less capable tool might suffice. For anyone who spends real time on detail work, the performance difference makes the investment worthwhile.

Construction project management in the UAE operates within a distinctive combination of regulatory requirements, commercial arrangements, and operational complexity that demands specialised software support. The bill of quantities sits at the centre of nearly every project financial process — from initial tender through to final account — while subcontractor management represents one of the most operationally demanding relationships a main contractor manages throughout a project’s life.

Addressing both of these functions within a unified ERP environment, rather than through disconnected point solutions, is the approach that leading UAE contracting businesses are increasingly adopting as they scale their operations.

Why BOQ Management Demands Specialist Software

A bill of quantities is more than a pricing document. It is the contractual basis for client billing, the framework for cost control, the starting point for procurement, and the reference document for variation order valuation throughout the project. Managing a BOQ in a spreadsheet environment means working with a document that does not automatically synchronise with any other business function — every change requires manual propagation, every report requires manual aggregation, and every reconciliation requires manual effort.

Specialist BOQ Software capability within an integrated ERP eliminates this manual overhead. The quantities and rates that form the BOQ are held in a structured database that connects directly to procurement, project cost management, client billing, and financial reporting. A variation approved in the commercial management function automatically updates the BOQ values, generates the variation order record, adjusts the project budget, and creates the billing entitlement — a workflow that in a disconnected environment might require updates to four or five separate systems.

Subcontractor Management: Complexity at Scale

For most main contractors in the UAE, subcontractors represent a significant proportion of project cost and a considerable management overhead. Subcontract agreements must be managed against the main contract scope, payment certificates must be processed in accordance with contractual terms and retention requirements, compliance documents must be tracked, and performance must be monitored against agreed programme and quality standards.

Effective subcontractor management software within an ERP context means that all of these functions operate from a single subcontractor record. The subcontract value and scope are defined against the relevant BOQ items. Progress is assessed against the subcontract schedule. Payment certificates are generated within the system and flow directly to the accounts payable process. Retention is calculated and held automatically. Compliance document expiry is tracked and flagged before it becomes a project risk.

The Integration Advantage

The most significant operational benefit of managing BOQ and subcontractor functions within an integrated ERP is the elimination of the information gaps that create problems in disconnected environments. When the quantity surveyor updates BOQ progress, those updates are immediately visible to the financial controller preparing monthly accounts. When the procurement team places a subcontract order, the commitment is immediately reflected in the project cost forecast. When a subcontractor payment is approved, the retention movement updates the retention account in real time.

A specialist ERP solutions company UAE delivers this integration as a core product capability rather than a custom development — meaning that the connectivity between functions is maintained through standard system updates and does not depend on the availability of specific technical resources to sustain.

Compliance and Reporting in the UAE Context

UAE contracting businesses operate under a regulatory framework that includes Federal Tax Authority VAT requirements, WPS payroll processing, and in many cases the reporting obligations associated with projects delivered for government or semi-government clients. An ERP system configured for the UAE market builds these compliance requirements into the core workflows — VAT is calculated and reported within the system, WPS files are generated from payroll processing, and project reports are formatted to client specifications without manual reformatting.

There is a version of IT management that many Australian businesses know well – the version where something breaks, someone panics, a technician is called, and everyone waits. It is reactive by design, expensive by outcome, and increasingly difficult to justify in a business environment where technology is no longer just a support function but a core part of how work gets done.

The shift toward managed IT services reflects a fundamental change in how businesses think about technology – not as a set of problems to be fixed, but as a capability to be maintained, developed, and aligned with business goals. For Australian organisations navigating growth, compliance requirements, and the demands of a distributed workforce, this shift is not just convenient. It is becoming essential.

The Hidden Cost of Breaking Down

Unplanned downtime is expensive in ways that are easy to underestimate. The obvious cost is the hours lost while systems are unavailable. The less obvious costs accumulate in the background – staff frustration, missed deadlines, client trust erosion, and the cascading effects of recovering from an outage that a routine monitoring check could have prevented entirely.

Research consistently shows that the cost of reactive IT support significantly exceeds the cost of proactive management when calculated across a full year. The emergency call-out rate, the premium charged for urgent repairs, the productivity lost while waiting for resolution – these costs are real and recurring, yet they rarely appear as a line item until someone sits down and adds them up.

This is one of the most compelling practical arguments for proactive managed IT services – the shift from responding to problems to preventing them. When your technology environment is continuously monitored, issues are identified and addressed before they escalate. The call you never have to make is worth more than the one that gets resolved quickly.

What Managed IT Services Actually Covers

The term managed IT services encompasses a broader range of capabilities than most people initially expect. At its core, it means transferring the ongoing responsibility for monitoring, maintaining, and supporting your technology infrastructure to a specialist provider – but the practical scope extends well beyond keeping the lights on.

Network monitoring and management keeps an eye on the systems that connect your business, identifying unusual traffic patterns, performance degradation, and potential security events before they cause problems. Security management – which has become the most urgent priority for most organisations – covers endpoint protection, threat monitoring, vulnerability assessments, and incident response planning. Cloud services management ensures that the platforms your business depends on are configured correctly, performing well, and scaling appropriately as your needs change.

Help desk and end-user support remains one of the most valued components for businesses that adopt managed support. When staff have a genuine, responsive resource to contact for day-to-day IT questions and issues, the friction of technical problems is reduced dramatically. Productivity does not grind to a halt while someone waits for a colleague to finish their own work before helping them reset a password or troubleshoot a connection issue.

The Security Dimension Has Changed Everything

Five years ago, cybersecurity was a concern primarily for large organisations with obvious high-value targets. That has changed. The volume, sophistication, and indiscriminate targeting of cyber threats has made every business with an internet connection a potential victim. Australian businesses of all sizes have experienced the consequences of insufficient security posture – ransomware, business email compromise, and data breaches that carry both financial and reputational consequences.

A quality managed IT support provider builds security into every layer of the service – not as an optional add-on but as a foundational component. This includes managing software patching and updates that close known vulnerabilities, implementing multi-factor authentication across systems, monitoring for suspicious activity, and maintaining the documentation and response plans that determine how quickly and effectively a business can recover if an incident does occur.

For Australian businesses subject to the Privacy Act and the Notifiable Data Breaches scheme, the compliance dimension of security management has become another practical reason to engage specialist support. Understanding what data you hold, how it is protected, and what your obligations are in the event of a breach requires both technical knowledge and regulatory awareness that most internal teams – particularly in small and mid-sized businesses – are not resourced to maintain independently.

Scalability and the Growth Problem

Technology infrastructure that works well for a business of fifteen people does not automatically scale to support a business of fifty. The cloud migrations, the additional user provisioning, the expanded network requirements, the more complex security considerations – growth creates IT complexity at a rate that frequently outpaces the capacity of an internal team to manage it.

This is where the scalability of a managed services model becomes particularly valuable. Rather than hiring additional internal IT staff ahead of growth – which commits to fixed costs before the revenue has arrived to support them – businesses can expand their managed services scope in step with their actual needs. The capability is there when it is needed, and the cost tracks with business activity rather than running ahead of it.

Vendor Management – The Invisible Workload

Managing the relationships with software vendors, hardware suppliers, internet service providers, and cloud platform operators is a significant ongoing workload that businesses often do not account for when they think about IT management costs. Licensing renewals, support escalations, contract reviews, and the coordination required when multiple vendors’ systems need to interact – this administrative overhead lands somewhere, and in most businesses without dedicated IT management, it falls on whoever happens to be most technically capable.

Managed IT providers handle vendor relationships as part of the service, acting as the single point of contact and accountability for the full technology stack. When something goes wrong that involves multiple vendors, the managed provider coordinates the resolution rather than the business owner spending hours on hold being passed between support teams.

Strategic IT Planning – Beyond Day-to-Day Support

The best managed service relationships evolve beyond operational support into genuine strategic partnership. Understanding a business’s goals, its growth trajectory, its regulatory environment, and its competitive context allows an IT partner to provide guidance on technology investment decisions that aligns with where the business is actually heading.

This strategic dimension – often described as virtual CTO or advisory services – brings IT decision-making capability to businesses that could not justify a full-time Chief Technology Officer but genuinely benefit from expert guidance on the technology choices that affect their competitive position. Should we move our file storage to the cloud? Are our current licensing agreements the most cost-effective option? Is our current infrastructure capable of supporting remote work at scale? These are business questions with technology answers, and having a trusted adviser who understands both dimensions makes a meaningful difference.

Choosing the Right Managed IT Partner

Not all managed IT providers offer the same scope, quality, or approach. When evaluating options, the questions worth asking go beyond price and coverage lists. How quickly does the provider respond to critical issues? What does their monitoring infrastructure actually look like? Can they demonstrate their security posture and not just describe it? Do they have experience with businesses in your industry and your scale?

References from existing clients – particularly those in similar industries – provide more useful insight than any amount of marketing material. A provider confident in their delivery will welcome the scrutiny.

For Australian businesses ready to make the shift from reactive to proactive technology management, partnering with an experienced managed IT services provider is the most reliable path to an IT environment that supports business performance rather than interrupting it. The investment in proper management pays dividends in uptime, security, and the confidence that comes from knowing your technology is being looked after by people who make it their entire focus.

Primary KW: ‘managed IT services’ | Secondary KW: ‘managed IT support’ | Anchor: ‘managed IT services provider’ | 1,100+ words